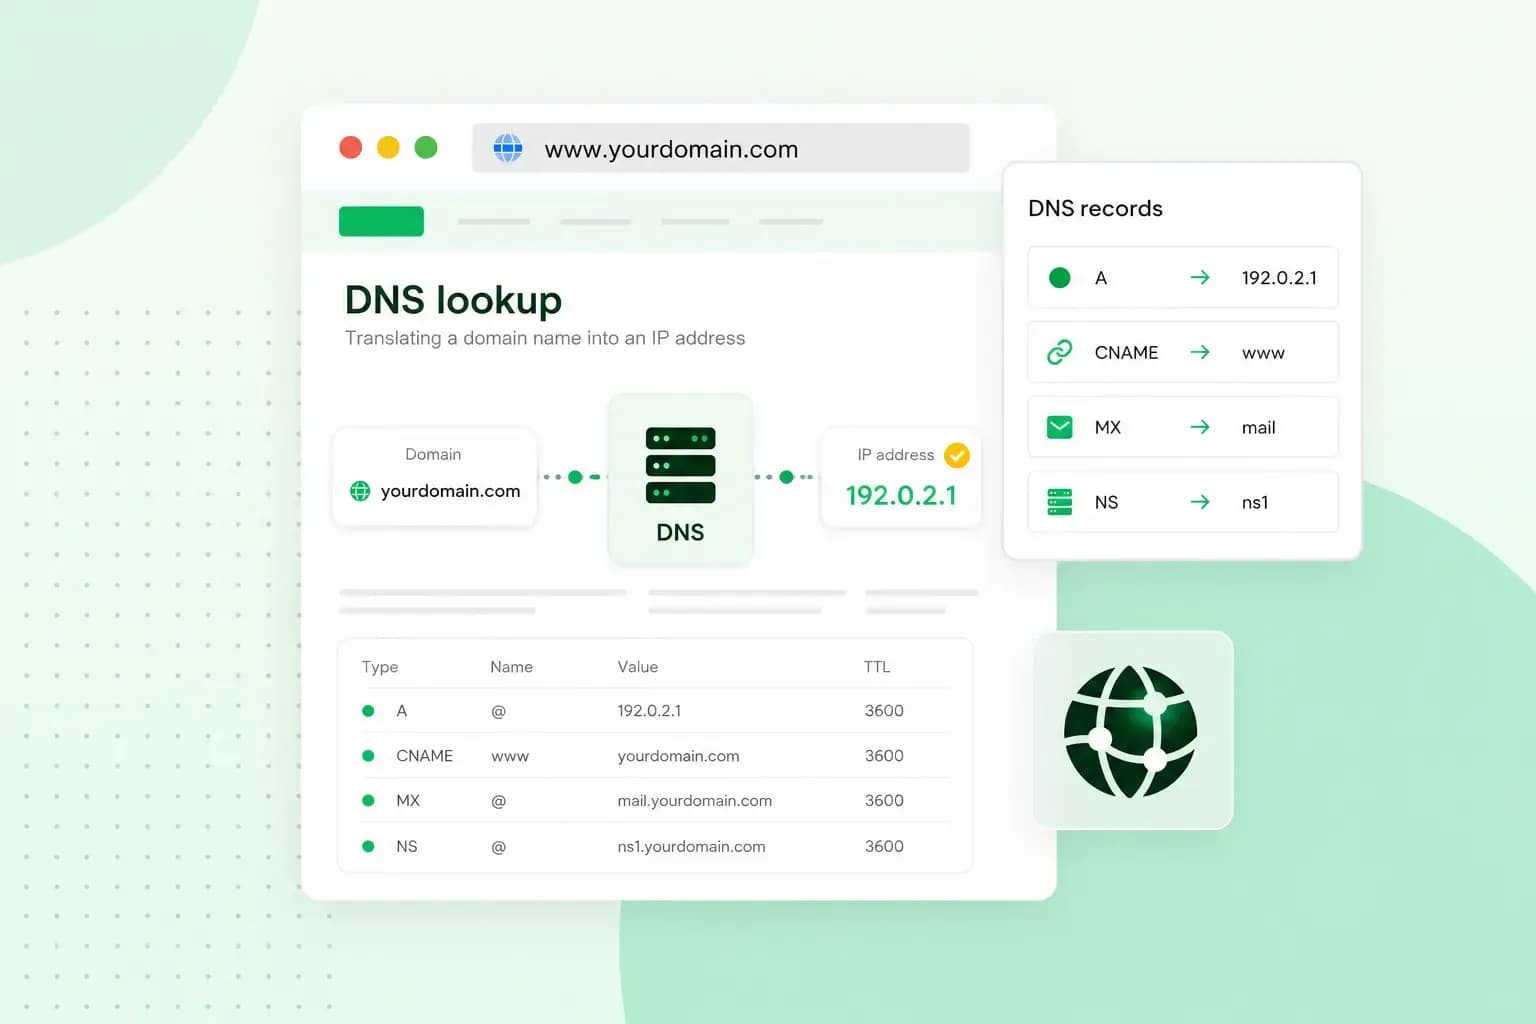
DNS, short for Domain Name System, is what turns a domain name into the IP address of the server a website sits on. The computers that do the looking up are called DNS servers. When you type an address such as yourbakery.co.uk into your browser, DNS servers find the matching number in the background. Your browser then loads the site.
Computers find each other by numbers, while people remember names. Every device on the internet has an IP address, a string of numbers that works like a phone number. DNS is the internet's phone book: you give it the name in the URL, and it gives your computer the number it needs.
What is a DNS server?
A DNS server, also called a domain name server or domain server, is a computer that turns a domain name into an IP address. There are two kinds, and each does a different job for you. A DNS resolver looks up addresses on your behalf: when you type yourbakery.co.uk, it goes and finds the IP address. Name servers hold the answers. They store each domain's DNS records, such as which server its website is on. The one that holds a domain's own records is its authoritative name server. You'll mostly meet the resolver as "my DNS server" in your network settings, and name servers when you set up your own domain.
How does DNS work?
DNS works by passing your request along a chain of DNS servers. It goes from the DNS resolver to a root name server, then a TLD name server and finally the authoritative name server for the domain. The first time you type yourbakery.co.uk into your browser, your device hands the request to the DNS resolver, and the lookup begins.
DNS resolver
The DNS resolver, also called a recursive resolver, takes your request. It's usually your internet provider's, although you can choose a public one instead. If it has looked up the address recently, it answers straight from its cache. If not, it asks the other servers one by one until it has the answer.
Root name server
Its first stop is a root name server, because root name servers sit at the top of DNS. They don't know where yourbakery.co.uk is. They do know which server handles each top-level domain, so they send the resolver on to the right one. There are 13 root name servers, labelled A to M and run by 12 independent organisations. Each letter stands for a network of machines rather than a single computer. On 22 October 2026, root-servers.org counted 2,048 of these machines in operation.
TLD name server
Next, the resolver asks the TLD name server, the name server for the top-level domain at the end of the address. For yourbakery.co.uk, that's the server for .uk domains, the UK's country code top-level domain. It doesn't hold the website's address either, but it knows which name servers are in charge of yourbakery.co.uk and points the resolver to them.
Authoritative name server
The last stop is the authoritative name server for yourbakery.co.uk. It holds the domain's own DNS records, so it gives the final answer: the website's IP address. For your own domain, that's a name server of whichever provider manages its DNS, whether that's us or another host. The resolver passes the address to your browser, and the website loads.
DNS records and your domain's DNS settings
Your domain's DNS records are the entries on its authoritative name server that tell the internet where to send visitors and email. Each type of record has its own job:
- A record: points your domain to the IPv4 address of the server your website is on. Most services still use IPv4 addresses.
- AAAA record: does the same for an IPv6 address, the newer format that is slowly replacing IPv4.
- CNAME record: makes one name an alias of another, for example to point a subdomain such as
shop.yourbakery.co.ukto a service hosted elsewhere. - MX record: tells other mail servers where to deliver email for your domain.
- TXT record: holds text that other services read, such as a domain verification code or the SPF and DMARC settings that help other mail servers check that email from your domain really comes from you.
- NS record: names the name servers that are in charge of your domain.
Our DNS settings also offer record types for special cases, such as SRV, CAA and TLSA records. Add one of these only when a service you use asks you to.
You change these records with the DNS provider your domain's name servers point to. That isn't always the company you registered the domain with. To find out which name servers your domain uses, check its settings where you registered it, in our control panel if you registered it with us. If you have a web hosting plan with us, your domain uses our name servers by default, ns01.one.com and ns02.one.com. You then manage your DNS settings in our control panel, where you can add records such as A, CNAME, MX and TXT yourself. Our name servers use anycast DNS, so most lookups of your domain reach whichever of our servers is closest on the network. If your domain uses another host's name servers, you manage its DNS settings with that host, even if we registered the domain for you.
Why DNS changes take time to show
A DNS change takes a while to reach everyone because of caching. Looking up every address from scratch each time would be slow. So your computer and the resolver keep, or cache, the answers they've had recently, which is why a site you visit often opens quickly. How long they may keep an answer depends on the record's time to live (TTL). On our name servers the TTL is one hour by default, and you can set it anywhere from 10 minutes to 24 hours.
After you change a record, a resolver that cached the old answer keeps using it until its TTL runs out. Until then, some visitors still see your old website. Each internet provider also updates through its own automated process. DNS propagation, the time a change needs to reach everyone, often takes a few hours and can take up to 72 hours. The TTL only decides how long one resolver keeps an old answer, not when every provider has the new one. A change of name servers can also take up to 24 hours before it's active. After that, like any DNS change, it can take longer to reach everyone.
If you're planning a move, lower the TTL to 10 minutes before you change the records. Do it at least one full TTL ahead: a day ahead if it's set to 24 hours, or an hour ahead at our default. By the time you change the records, resolvers have picked up the shorter TTL.
What is my DNS server?
Your DNS server is the resolver your device uses, and your internet provider usually sets it automatically when you connect. To see which one you're using, open the test site Browserleaks and choose its DNS Leak Test. It lists the DNS servers your browser sends its lookups to.
As long as websites load normally, your provider's resolver is doing its job and there's usually no need to change it. Some people still switch to a public DNS service, such as Google Public DNS. Google believes its service gives more accurate answers, better security and, in most cases, faster lookups. You switch by entering the service's IP addresses as the DNS servers in your device's network settings. Google's guide to using Google Public DNS lists its addresses with the steps for each system. It asks you to write down your current DNS settings first, so you can go back to them. From then on, your device sends its lookups to that service instead of your provider's, so the service sees which sites you look up. Choose one whose privacy policy you're happy with.
When websites suddenly stop loading, try restarting your router or opening the site on another device first. If you still get a DNS not responding error, our guide takes you through the next fixes.
How to keep your domain's DNS safe
Because visits to your website rely on DNS, attackers target DNS. In DNS cache poisoning, also called DNS spoofing, an attacker slips false records into a resolver's cache. The resolver then sends visitors to a fake website instead of the real one, where their personal details can be stolen.
Against cache poisoning, you can use DNSSEC for your domain. It adds digital signatures to your domain's DNS records. Resolvers can then check that an answer comes from the right name server and hasn't been tampered with on the way. If your domain uses our name servers, DNSSEC is on by default.
Domain Lock guards against a different risk: it locks your domain, so nobody can transfer it to another registrar without your permission. It's an add-on you can buy for a domain registered with us.
Put your own domain's DNS to work
A website and email on your own domain rest on two of the records above. The A record points the domain to the server your website is on, and the MX record decides where your email goes. On our name servers, the MX record points to our mail servers by default, so with email from us there's nothing to change. If your email is hosted elsewhere, you point the MX record to that provider instead.
With a domain from us, you can manage its DNS records in our control panel even without a hosting plan, and point it at a website hosted elsewhere.
Buy your domainThe answer to every lookup of your address starts from the records on your domain's name servers, so that's where your website and email begin. If you don't have a domain yet, register your own domain with us and point its records to wherever your website and email are hosted.
Recommended reading
 DomainOct 2, 2026
What is a .si domain?
 DomainSep 9, 2026
How to choose a domain name
With the abundance of websites on the internet, choosing a domain name can be overwhelming. Continue reading for some tips & tricks on how to pick yours. DomainAug 5, 2026
Domain names and SEO: what you should know
Start your website off on the right foot by choosing a domain name that will boost your website’s visibility on search engines.